Case Files
P1Security vulnerabilityPHP2Shell
PHP2Shell: Early flagged the defect in the change that introduced it.
Early flagged the PHP2Shell memory-lifetime defect and a separate initialization bug in a replay of the January 2025 change. In a follow-up on the vulnerable revision, Early created a Fix PR for the backtrace defect.
What changed
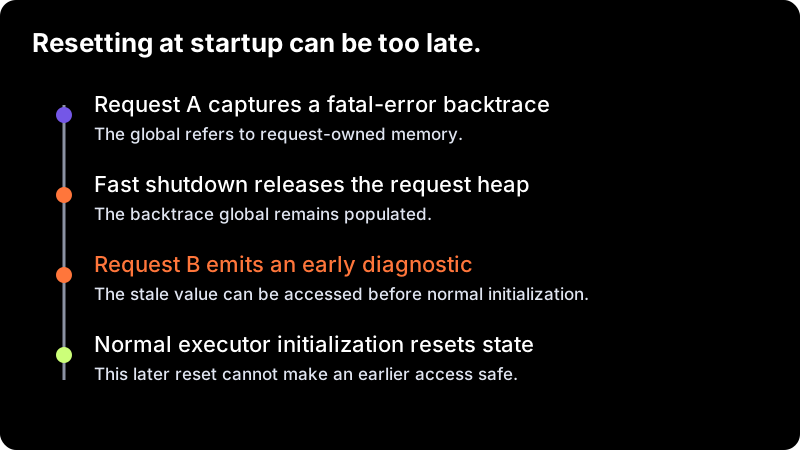
A later error could access freed request memory.
The analysis run
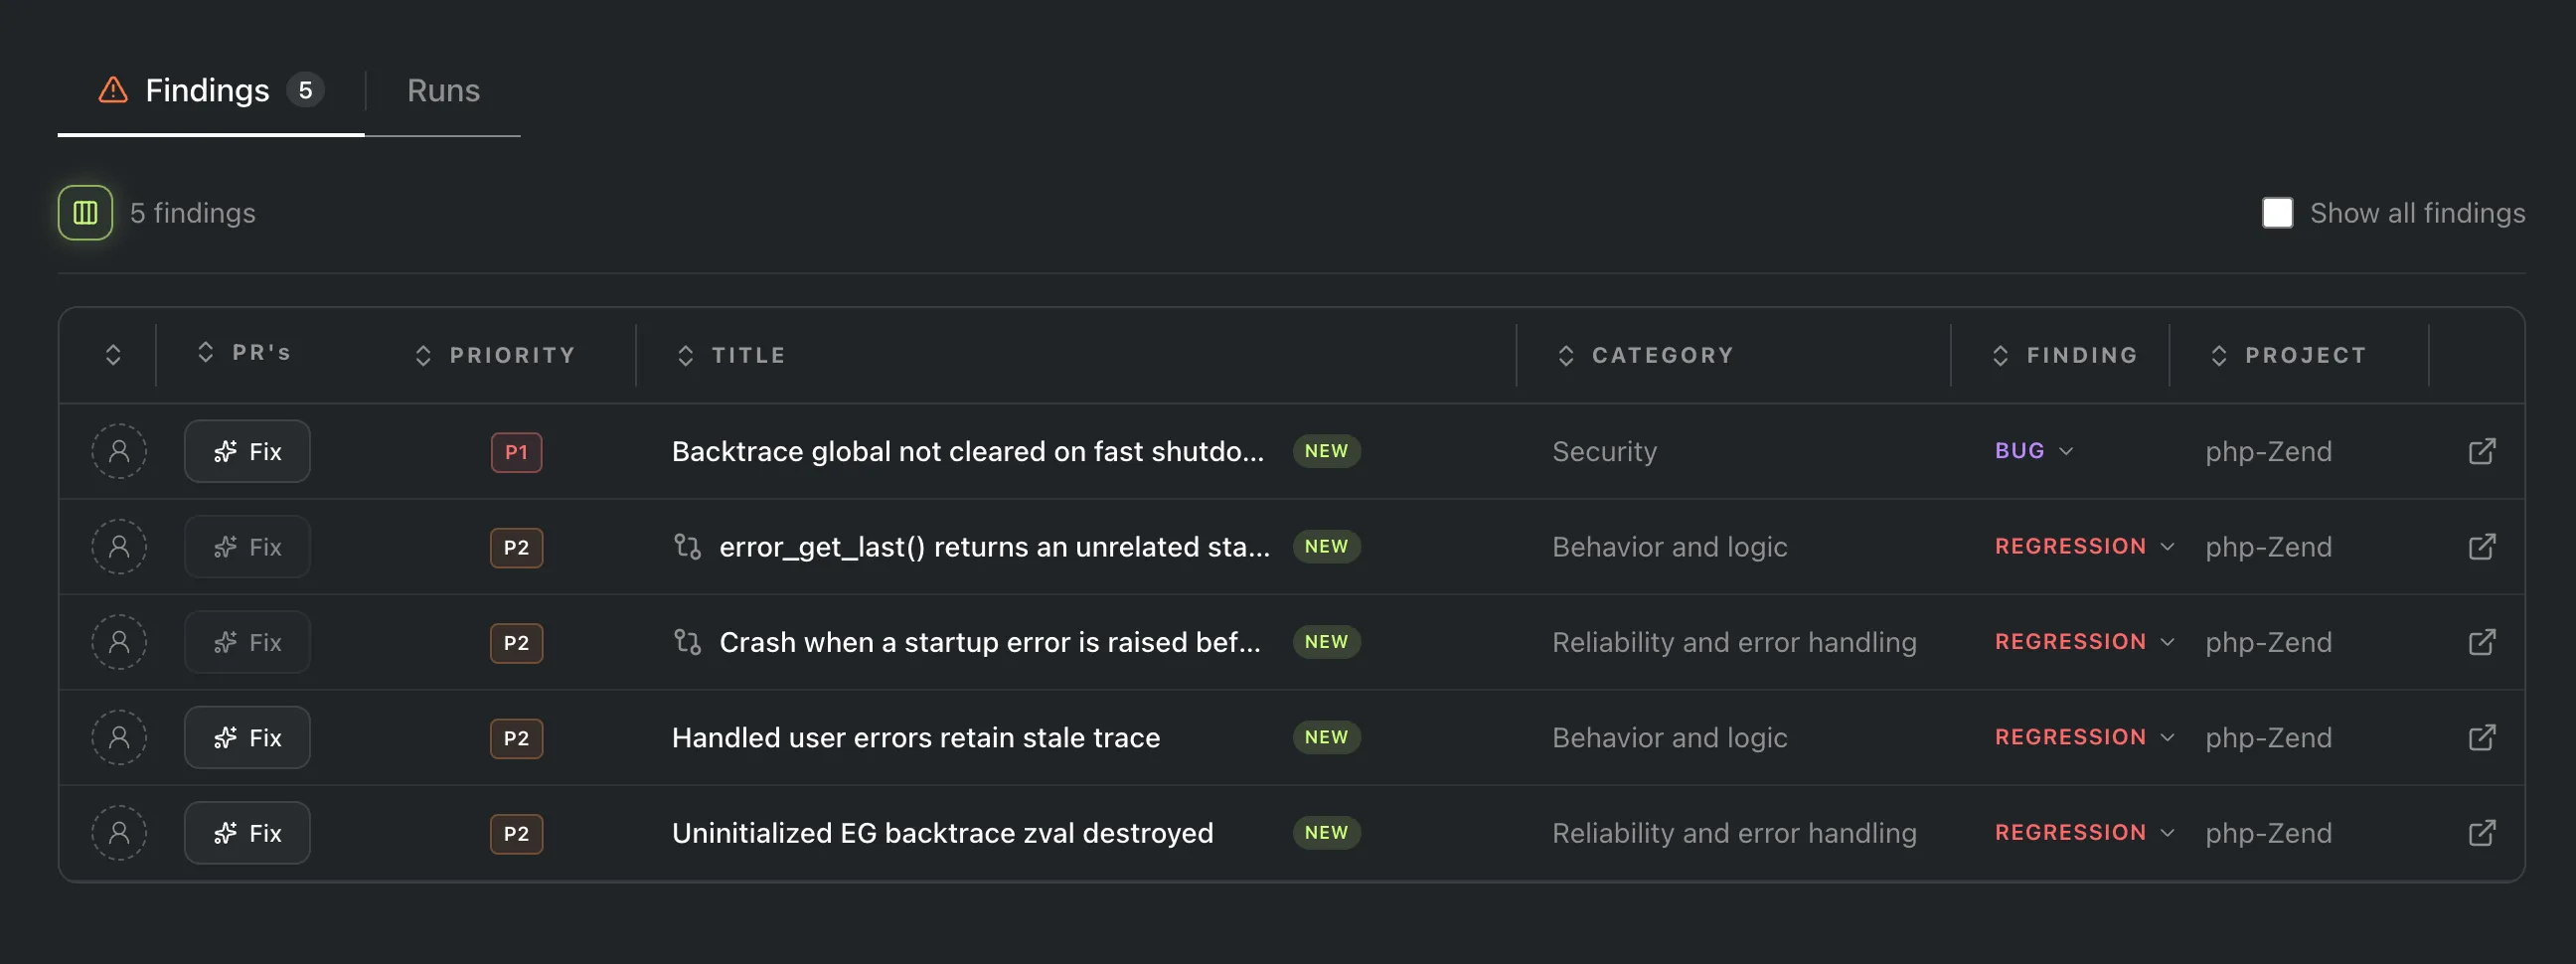
3 findings surfaced for action.
Early analyzed the January 2025 Zend change and flagged the backtrace defect alongside two other actionable findings.
The PHP2Shell finding
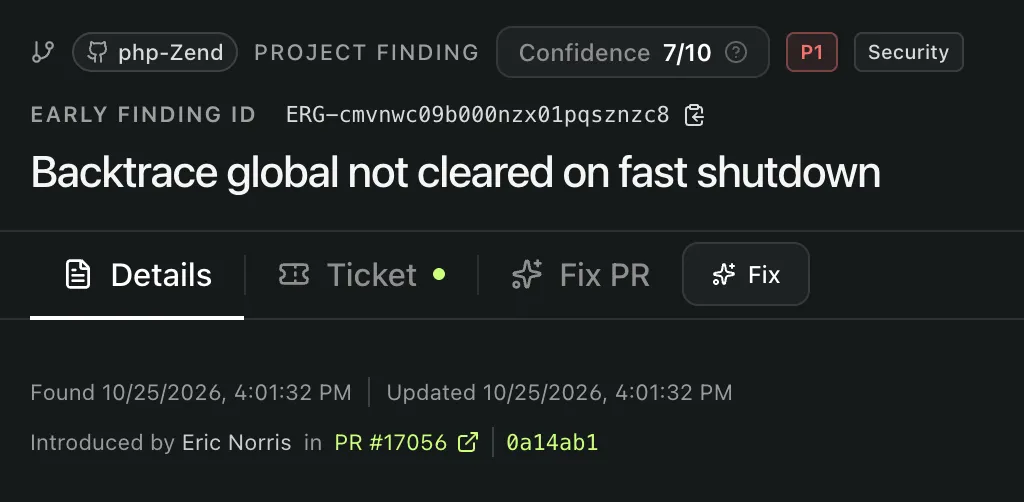
Early flagged the memory defect.
Early verdict · BUG
“Backtrace global not cleared on fast shutdown”
Early pointed engineers to the shutdown cleanup path and the stale reference it left behind. Fast shutdown could free the request’s memory while the backtrace global still pointed to it. An early error in a later request could reach that freed memory.
From finding to Fix PR
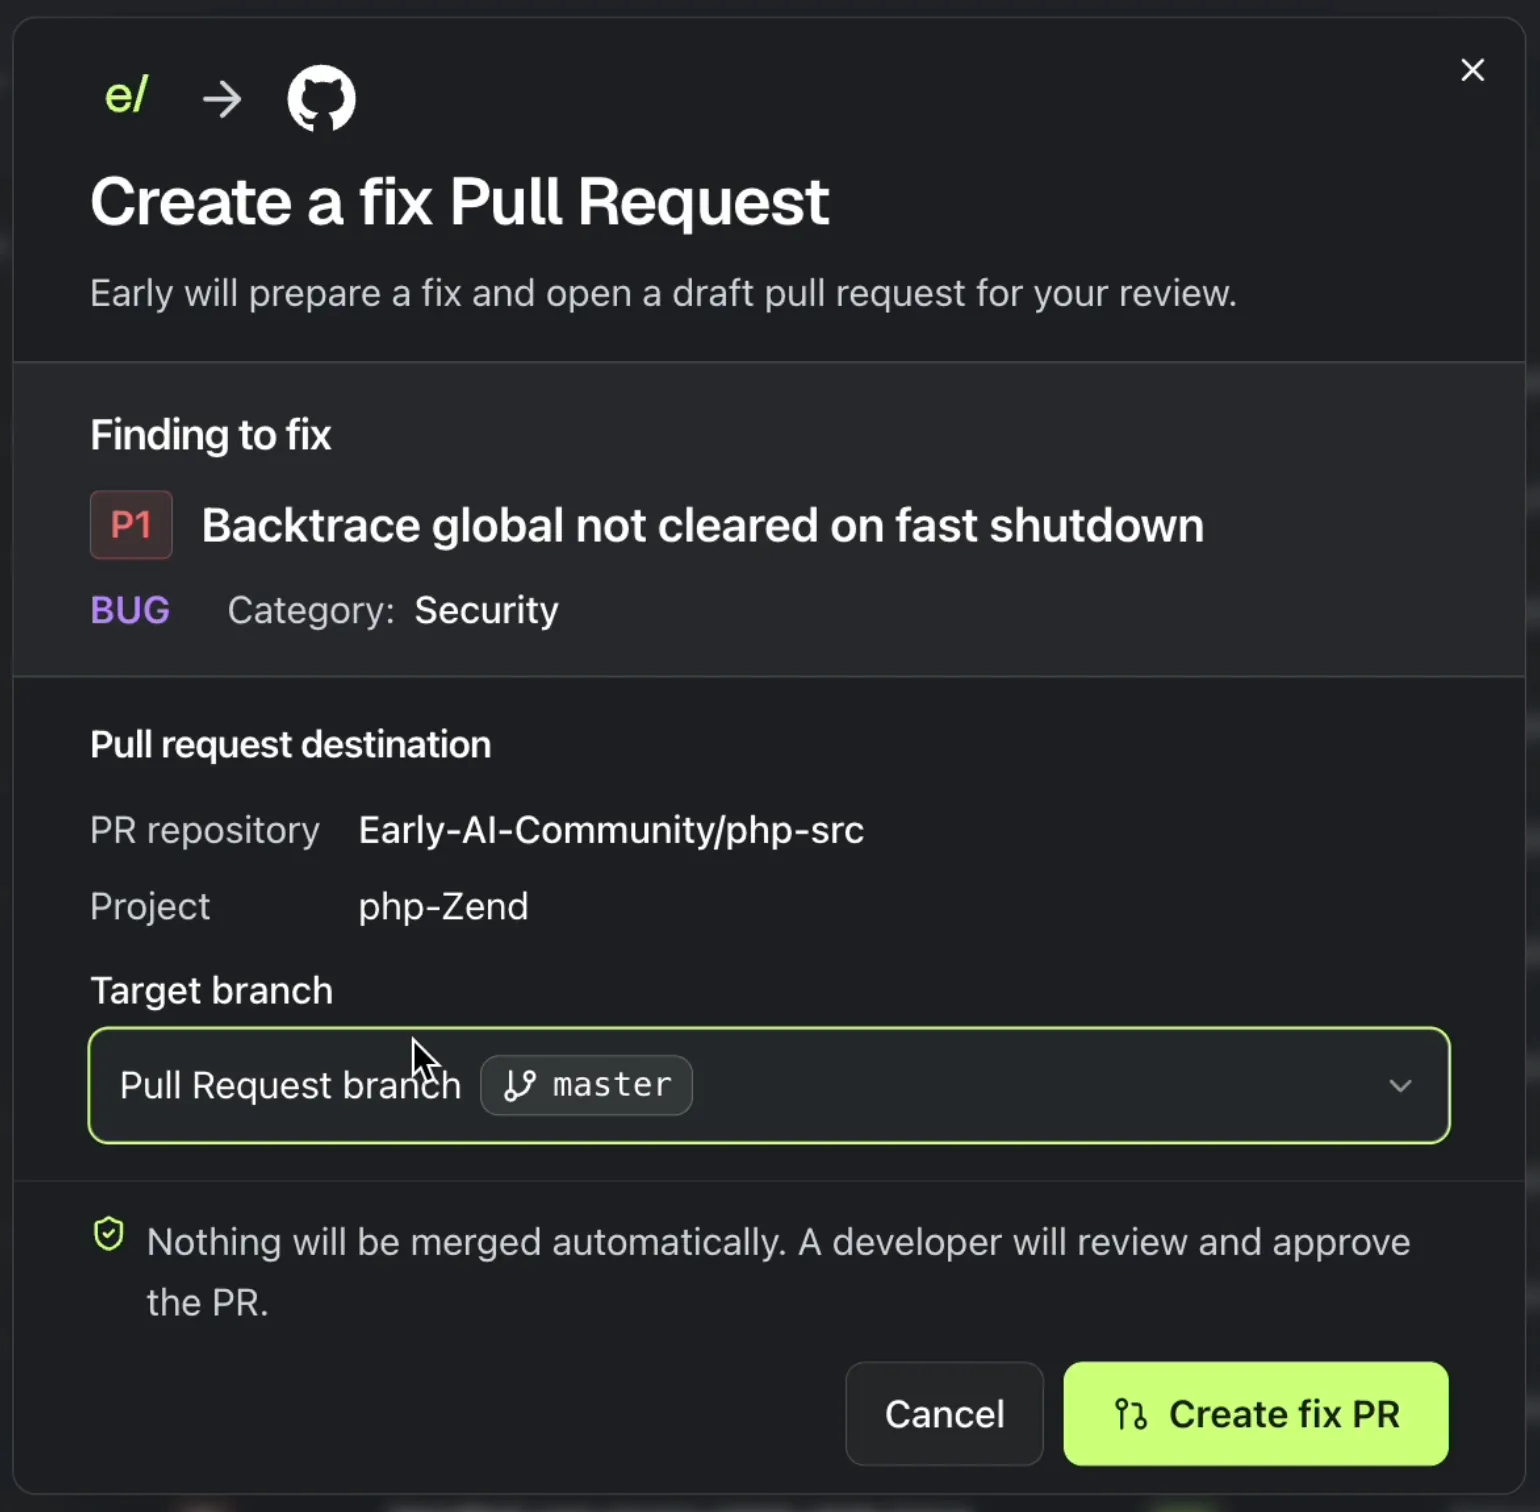
Early created a Fix PR that clears the stale backtrace reference during shutdown.
ZVAL_UNDEF(&EG(last_fatal_error_backtrace));Compilation/runtime verification pending · No new test added
- Fix PR createdWith a test
 Early Found a Credential Leak. Pydantic Shipped the Fix.
- 3 releases247 hours to fix
 Mastra output processor regression
- 1 release~18 hours to fix
 Rspack CommonJS export regression
- 1 release~20 hours to fix
 Conan no-op replacement regression
- 3 releases12 days to fix
 Hono form parsing regression